Insights
Field notes on AI strategy, governance, and execution.
Editorial note: Research and drafting are AI-assisted. Methodology claims, regulatory citations, and recommendations are grounded in documented research — every article includes specific source references. Daniela Piskackova — Co-founder & AI Audit Lead — is the research methodology guarantor behind our work. This transparency matches who we are: an AI-native company.
GDPR Article 27: when a US company needs an EU representative
Assess whether GDPR Article 27 requires your US company to appoint an EU representative, test the narrow exemption, and document the representative's role.
Processing under GDPR: What Counts in Plain Terms?
Processing under GDPR includes collecting, viewing, storing and deleting personal data. Use this practical check to decide what your organisation must record.
ICO guidance on AI and data protection for UK firms
ICO guidance on AI and data protection asks UK firms to map data uses, choose lawful bases, assess DPIA risk, explain decisions and document vendor roles.
Standard contractual clauses: when do you use them?
Decide when EU standard contractual clauses are needed, choose the correct transfer module, assess Clause 14 and complete the annexes before signing.
ICO registration: who pays the 2026 data protection fee?
ICO registration in 2026: check whether your UK business owes the data protection fee, which activities may be exempt, how tiers work, and when to renew.
Subject access request time limit under UK GDPR: DUAA
Calculate a UK subject access request time limit after the DUAA: when one month begins, when clarification pauses it, when it resumes, and when it extends.
Automated decision making GDPR: UK rules after DUAA
Automated decision making under the UK GDPR changed after the DUAA. Test significant decisions, lawful bases, special category data and human challenge routes.
ICO fines in 2026: recent UK cases and how amounts are set
Compare recent UK ICO fines for a water utility and unlawful marketing texts, then follow the five steps used to calculate a data protection penalty.
Data Subject Rights: How to Handle Every GDPR Request
Data subject rights explained: one-month deadlines, access copies, erasure, portability, marketing objections, refusals and a practical request log.
Is a Name Personal Data? Certificates and Lists Explained
Is a name personal data? Use identity, context, content and filing tests for certificates, attendance sheets and paper lists under data protection law.
Outsourced DPO or In-House DPO: A UK Decision Guide
Outsourced DPO or in-house DPO? Test the legal trigger, expertise, independence, conflicts, resources and practical access for a UK company.
DPO's Duties: Does Your UK Company Actually Need a DPO?
DPO's duties under UK GDPR: the three appointment triggers, core tasks, independence, conflicts and the record needed when no DPO is appointed.
GDPR Fines Explained: Amounts, Tiers and How They Are Set
GDPR fines have two statutory ceilings, but the final amount depends on the infringement, turnover and the authority's case-by-case assessment.
Cookie compliance: what a UK banner must do in 2026
Cookie compliance under PECR changed on 5 February 2026. Learn which cookies need consent, what the banner must offer and what evidence to retain.
What Is a Data Protection Impact Assessment (DPIA)?
A data protection impact assessment identifies and reduces high risks before processing starts. Learn its triggers, contents, review and consultation rules.
GDPR for WordPress: Plugins, Forms and Analytics in the UK
GDPR for WordPress means mapping data, fixing forms and notices, controlling cookies, checking processors and transfers, and maintaining site security.
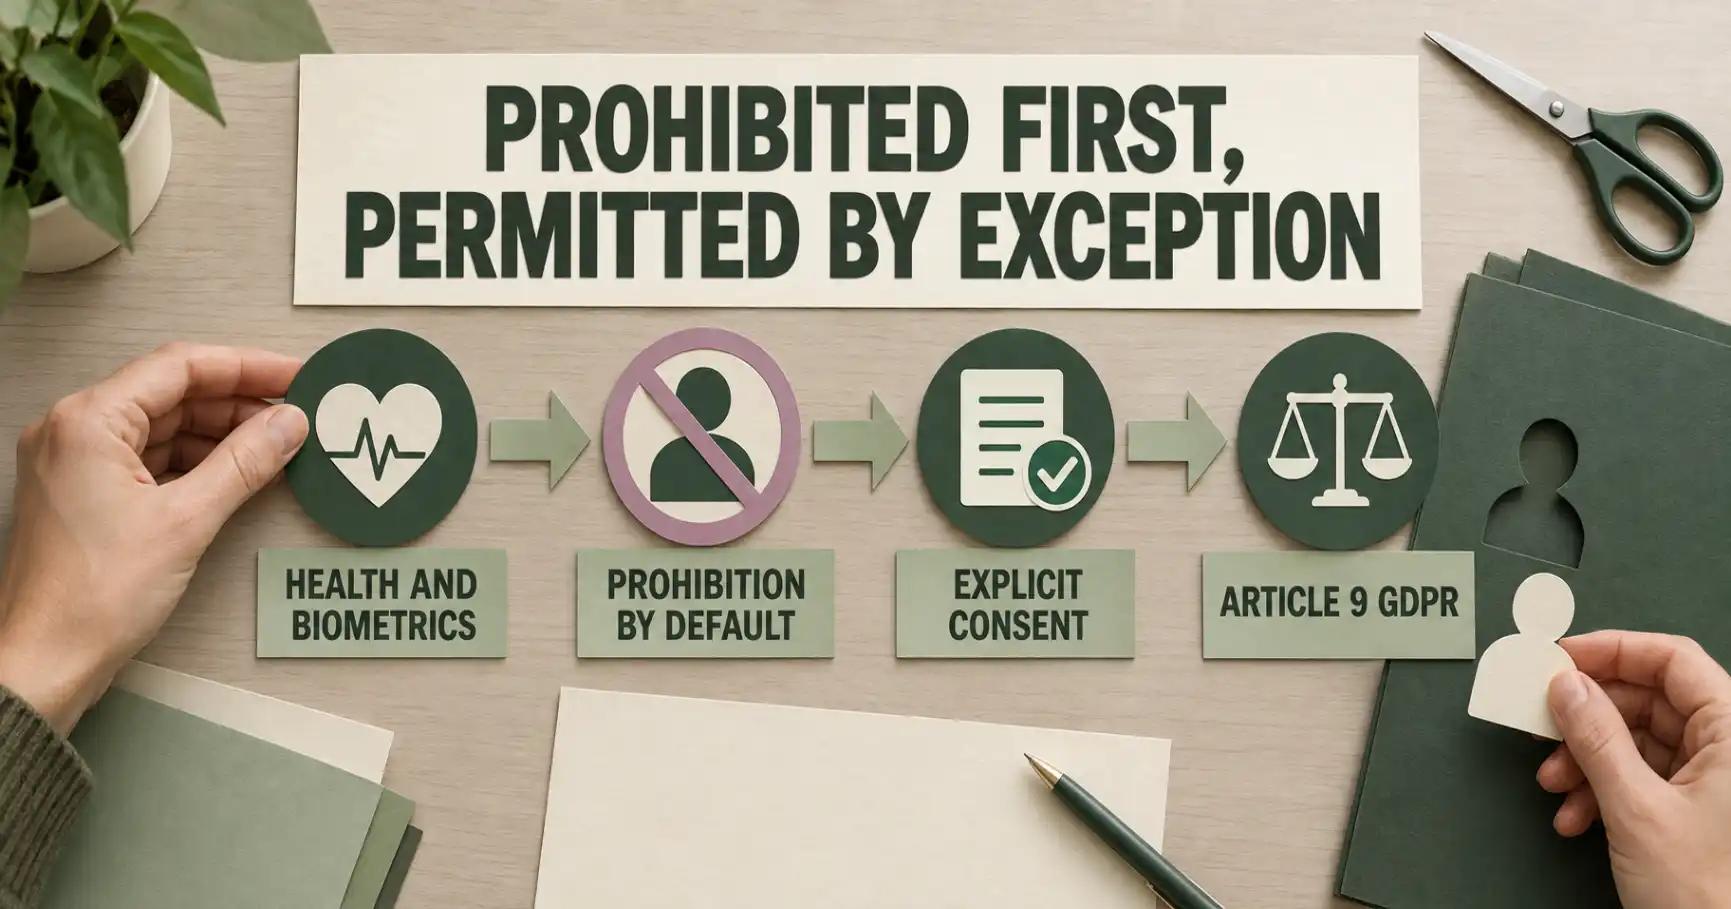
Special category data: what counts and extra rules
Special category data is protected by Article 9 GDPR. Learn which data qualifies, when processing is permitted and which extra safeguards apply.
Can I Email Businesses Without Consent in the UK? Send or Hold
Can I email businesses without consent in the UK? See which subscribers qualify, when consent or soft opt-in is needed, and the checks to record before sending.
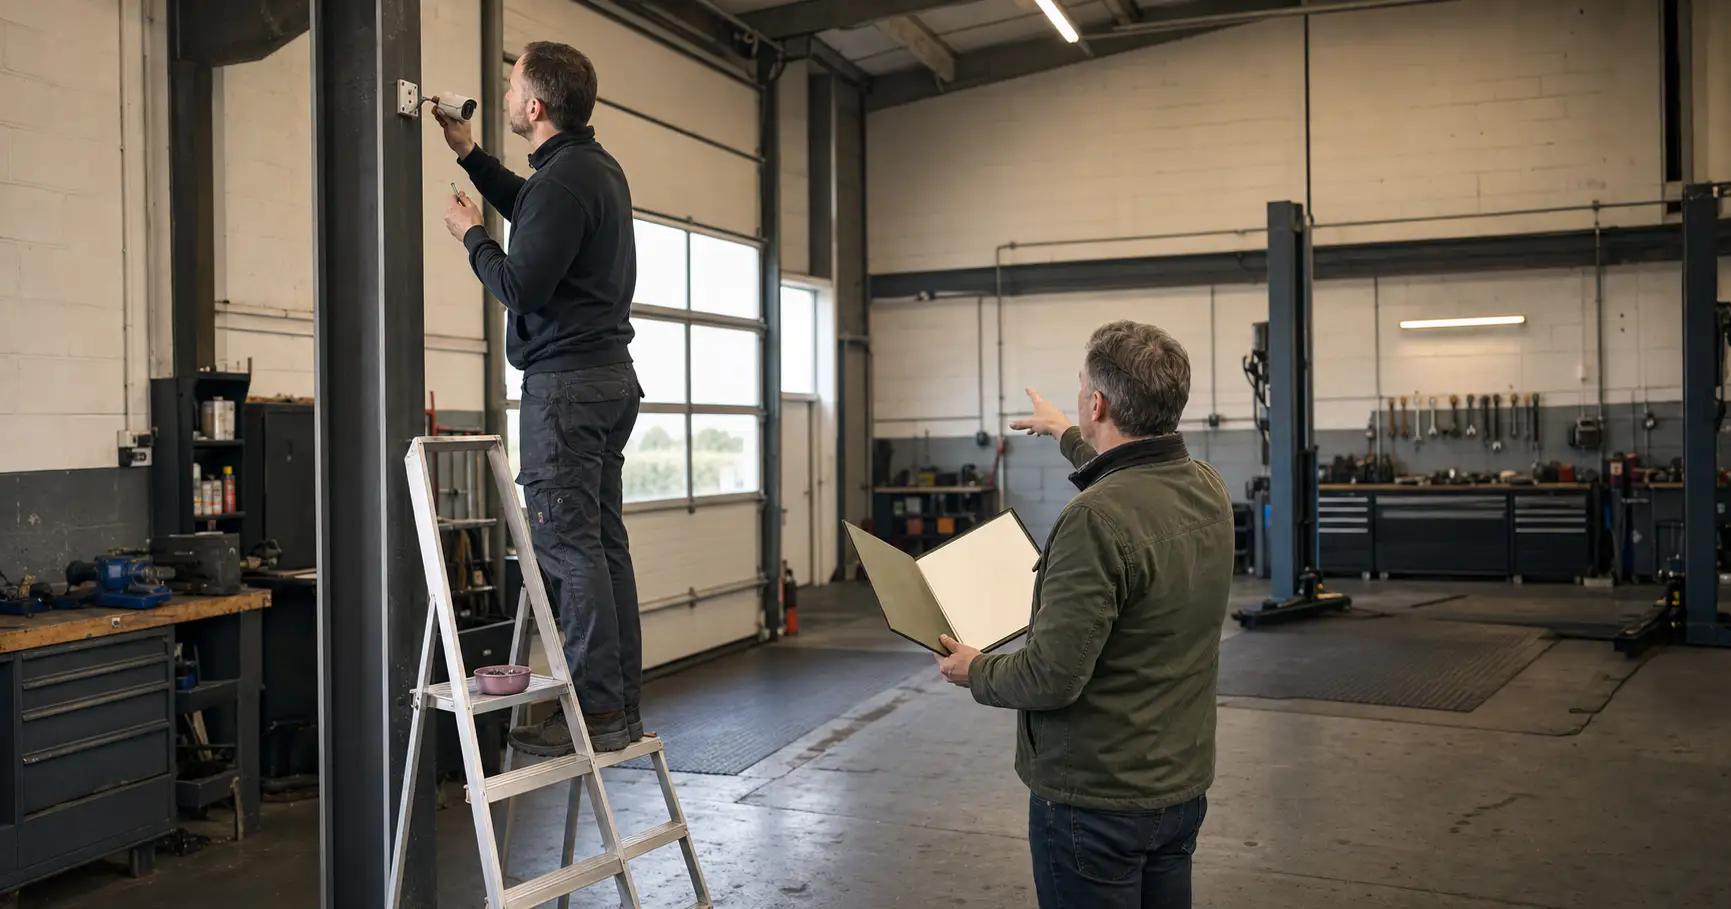
CCTV Monitoring Employees: UK Law and Practical Steps
CCTV monitoring employees under UK law: define the purpose, assess necessity, complete any required DPIA, inform workers and control footage and access.
Controller or Processor? A Practical EU Activity Test
Use a per-activity test to decide controller, processor or joint control, then choose the right GDPR agreement and record the reasons clearly.
Cookie Banner Requirements for UK Small Businesses
Cookie banner requirements for UK small businesses: classify cookies, block consent-required scripts, obtain real consent and test reject and withdrawal paths.
Data Processing Agreement Guide for EU Small Businesses
A practical data processing agreement for an EU small business: map the service, compare terms, use the free Commission clauses, complete annexes and test it.
Do I Have to Delete Data from Backups Under the GDPR?
Do I have to delete data from backups? Apply Article 17, separate active and recovery copies, control restores, and retain evidence for each decision.
Data Protection Officer Requirements: When Is a DPO Mandatory?
Data protection officer requirements use three GDPR tests and national law. Decide whether to appoint a DPO, then document and revisit the outcome.
Do You Need a Data Protection Officer? UK Rules Explained
Do you need a data protection officer? Apply the UK GDPR tests, compare business examples, and record a defensible answer for either outcome.
Does GDPR Apply Outside the EU? The Article 3 Test
Does GDPR apply outside the EU? Test EU establishment, targeted offers and monitoring, then decide whether an Article 27 representative is required.
Does UK GDPR Apply if Customers Are Outside the UK?
Does UK GDPR apply if customers are outside the UK? Test establishment and targeting, then assess representatives, transfers and any parallel EU GDPR scope.
GDPR Templates for Small Businesses: The Honest Minimum
GDPR templates small business teams can use: six living core records, conditional overlays, free EU clauses, and a practical test for generic packs.
How Long to Keep Personal Data in the UK: Set Each Period
How long to keep personal data in the UK: separate accounting, payroll and other records, set defensible periods, and plan deletion across backups.
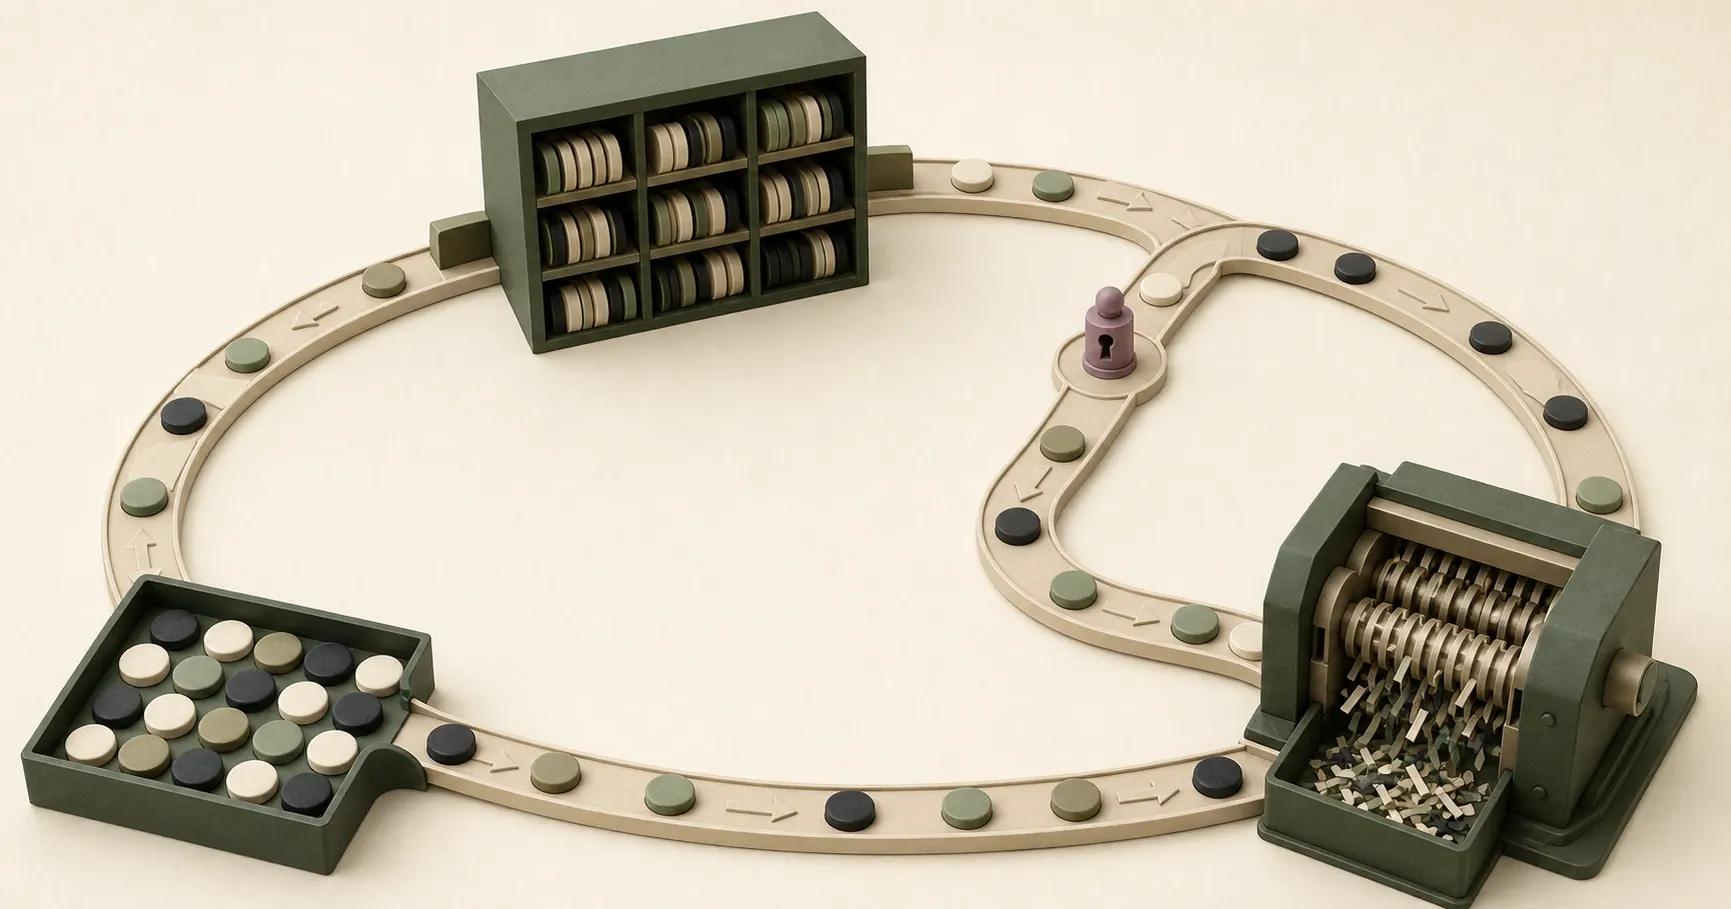
How Long to Keep Personal Data Under EU GDPR: A Practical Guide
How long to keep personal data under EU GDPR: identify each legal driver, set defensible retention periods, manage backups and delete records in practice.
Is Business Contact Data Personal Data? An EU Field Test
Is business contact data personal data? Classify named work details, generic inboxes and business forms, then separate GDPR duties from marketing rules.
Is GDPR Really a Problem for a Small Business in the UK?
Is GDPR really a problem for small business? See what 99 recent ICO actions show, what usually goes wrong, and which minimum UK controls matter in practice.
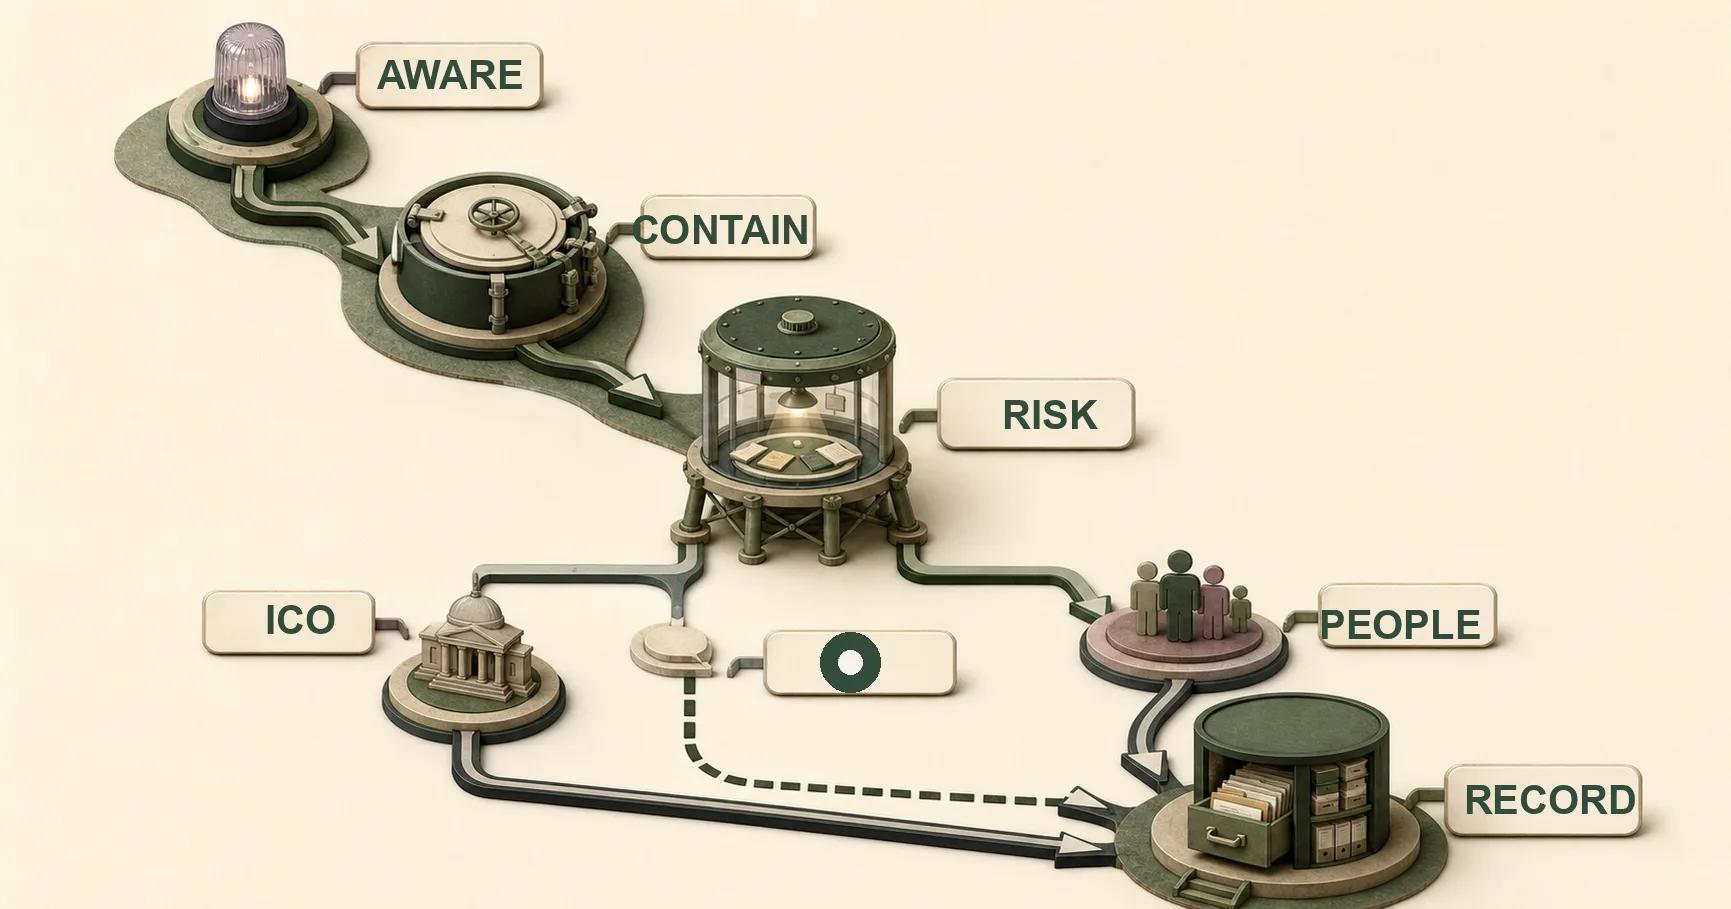
Is This a Reportable Data Breach in the UK? Decide Fast
Is this a reportable data breach in the UK? Start the 72-hour clock at awareness, assess risk, record the decision and notify people if high risk.
Is This a Reportable Data Breach Under EU GDPR? A Decision Guide
Is this a reportable data breach? Start the 72-hour clock at awareness, assess risk, document the decision and notify the competent authority when required.
Legitimate Interests vs Consent in the UK: How to Choose
Legitimate interests vs consent in the UK: use the purpose, necessity and balancing tests, check PECR, and record why the chosen lawful basis fits.
Legitimate Interests vs Consent Under EU GDPR: How to Choose
Legitimate interests vs consent under EU GDPR: apply purpose, necessity and balancing tests, check ePrivacy rules, and record why the chosen basis fits.
GDPR Records of Processing Activities: Article 30 Guide
GDPR records of processing activities must follow Article 30 role-specific fields. Build a living record and test the narrow under-250 exception.
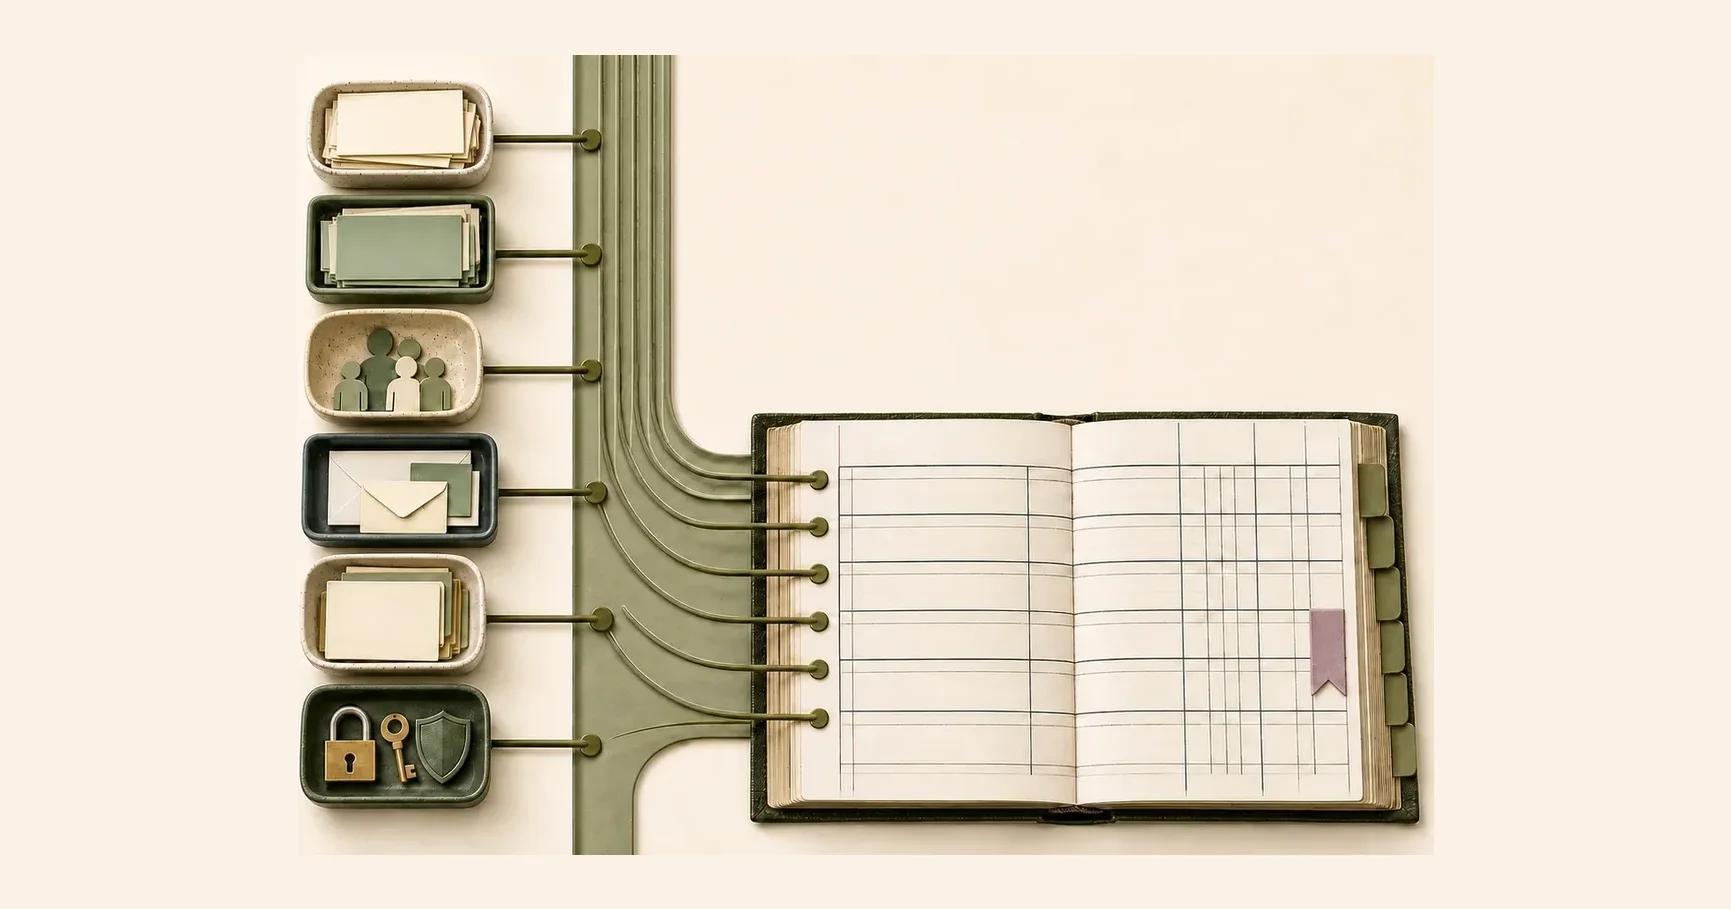
Records of Processing Activities: UK Article 30 Guide
Learn which records of processing activities UK GDPR Article 30 requires, what each record must contain, and how to build and maintain yours.
UK GDPR Small Business Guide: What to Do First in 2026
A practical UK GDPR small business guide: map personal data, choose lawful bases, write usable records, handle rights, secure data and review the system.
What Is a Lawful Basis? Seven UK GDPR Routes Explained
What is a lawful basis under UK GDPR? Compare all seven routes, avoid treating consent as the default, and record the basis that fits each purpose.
What Is a Lawful Basis? Choose the Right EU GDPR Route
What is a lawful basis under EU GDPR? See the six routes, when consent is unnecessary, and how to assess, record and explain the right basis for each use.
What Is a Personal Data Breach? EU GDPR Explained Clearly
What is a personal data breach under EU GDPR? Recognise confidentiality, integrity and availability failures, then take the right first-hour steps.
What Is a Subject Access Request? The UK GDPR Rules Explained
What is a subject access request under UK GDPR? Recognise one without magic words, start the one-month clock, search properly and respond lawfully.
What Is a Subject Access Request? An EU GDPR Guide
What is a subject access request under EU GDPR? Recognise one without magic words, start the one-month clock, search completely and respond lawfully.
What Must a Privacy Notice Say Under the EU GDPR Rules?
What must a privacy notice say? Compare Articles 13 and 14 GDPR, check every required field, fix timing, and retain practical evidence of delivery.
When Is a DPIA Required? Reach a Reasoned Yes or No
Decide whether you need a DPIA before processing: test Article 35 cases, nine risk criteria and authority lists, then record and review a reasoned yes or no.
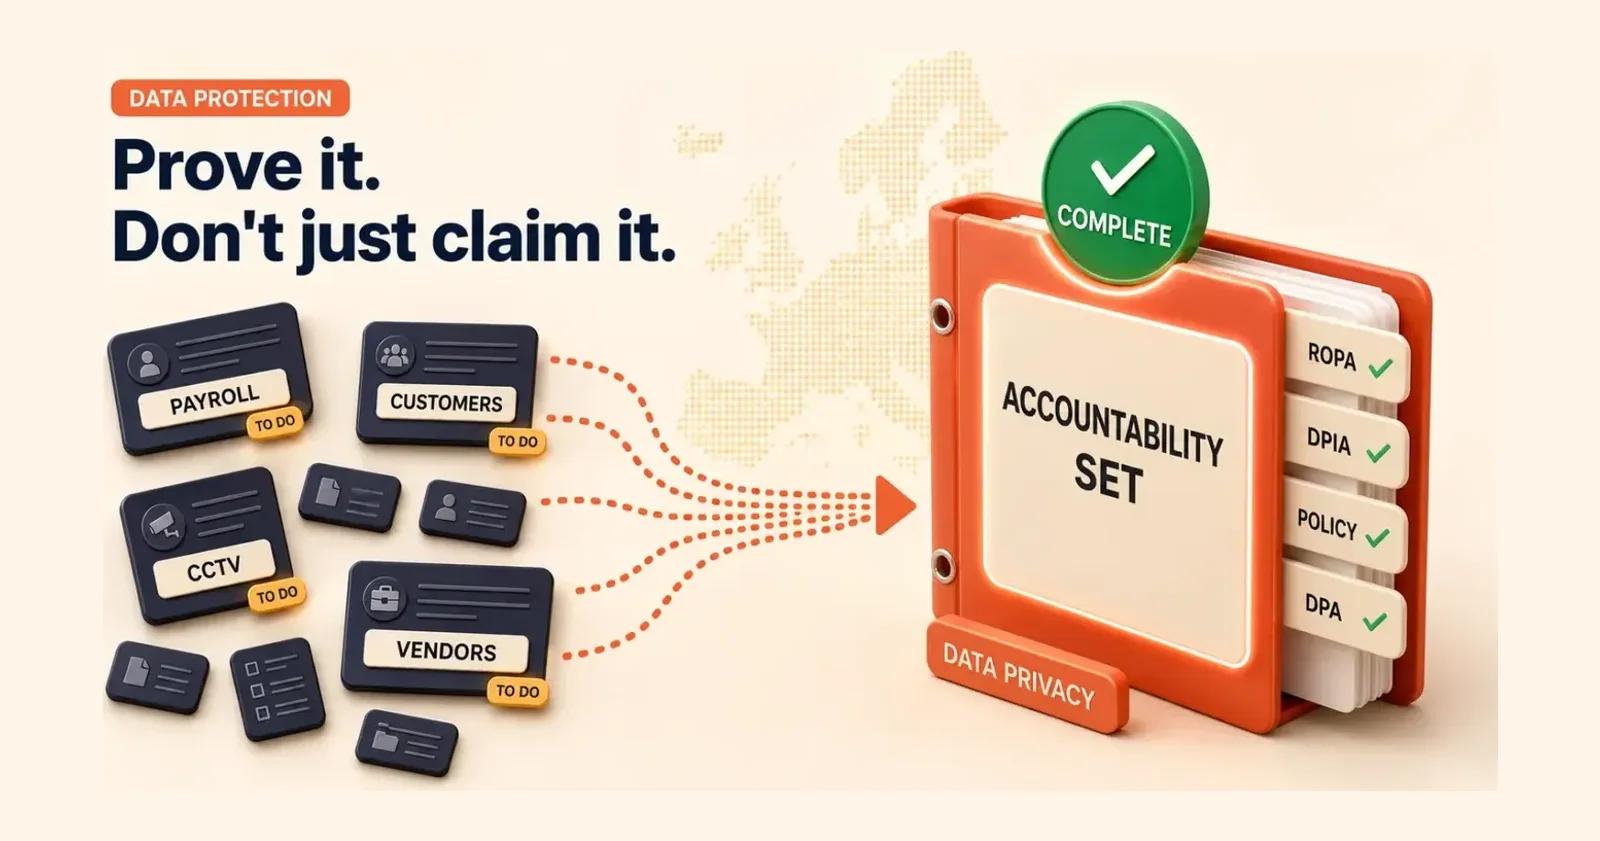
GDPR Accountability: What EU Companies Must Document
GDPR accountability means proving compliance rather than claiming it. The records EU companies must hold — ROPA, DPIA, policies — and how to build the set.
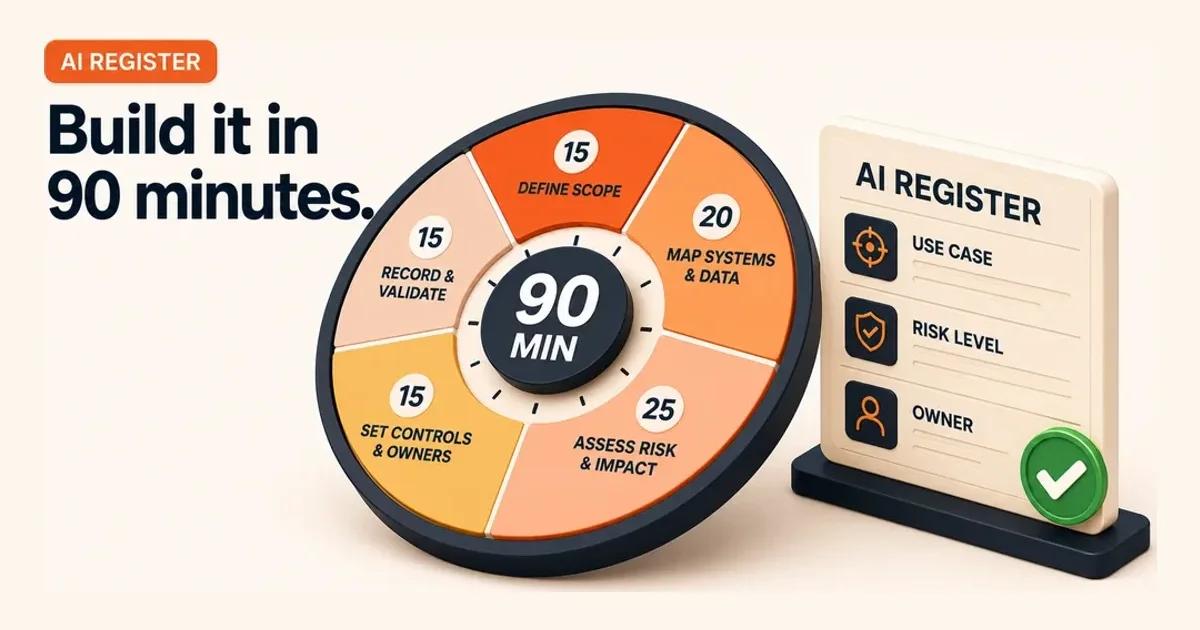
How to Build an AI Register in 90 Minutes (EU AI Act)
How to build an AI register in ninety minutes, before the Article 26 deployer duties begin to apply in December 2027: the five steps, the starter columns, the owner rules and the pitfalls.
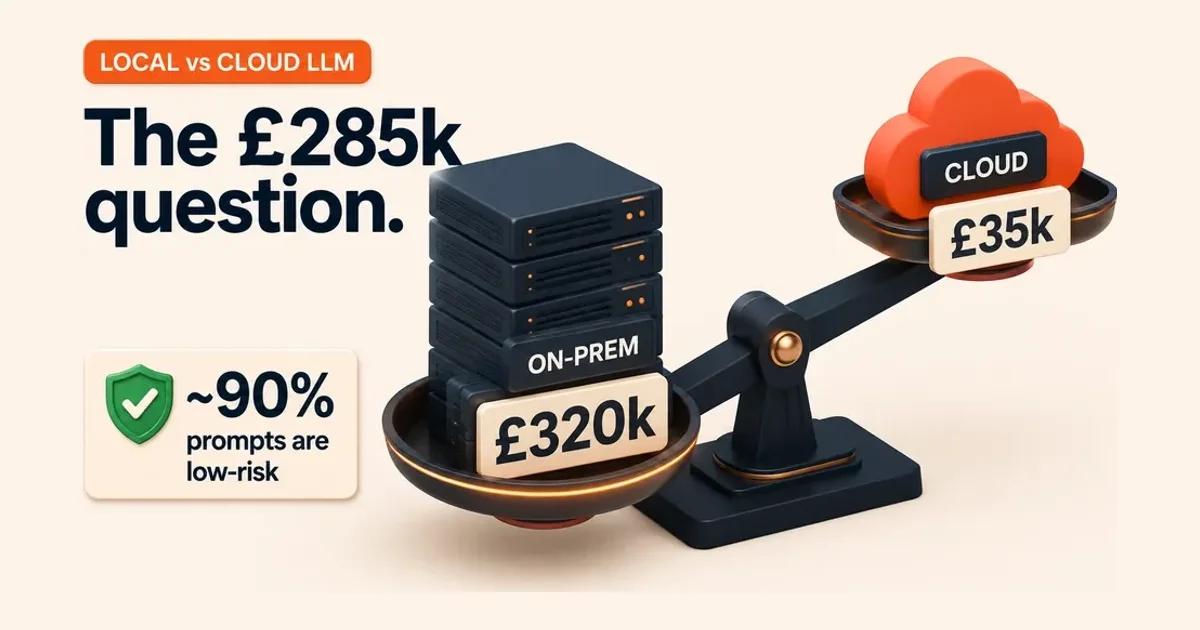
Local LLM vs Cloud LLM Data Security: The Wrong Question (2026)
Local LLM vs cloud LLM data security is the wrong question: the real leak is staff pasting into personal accounts, which a local model never touches.
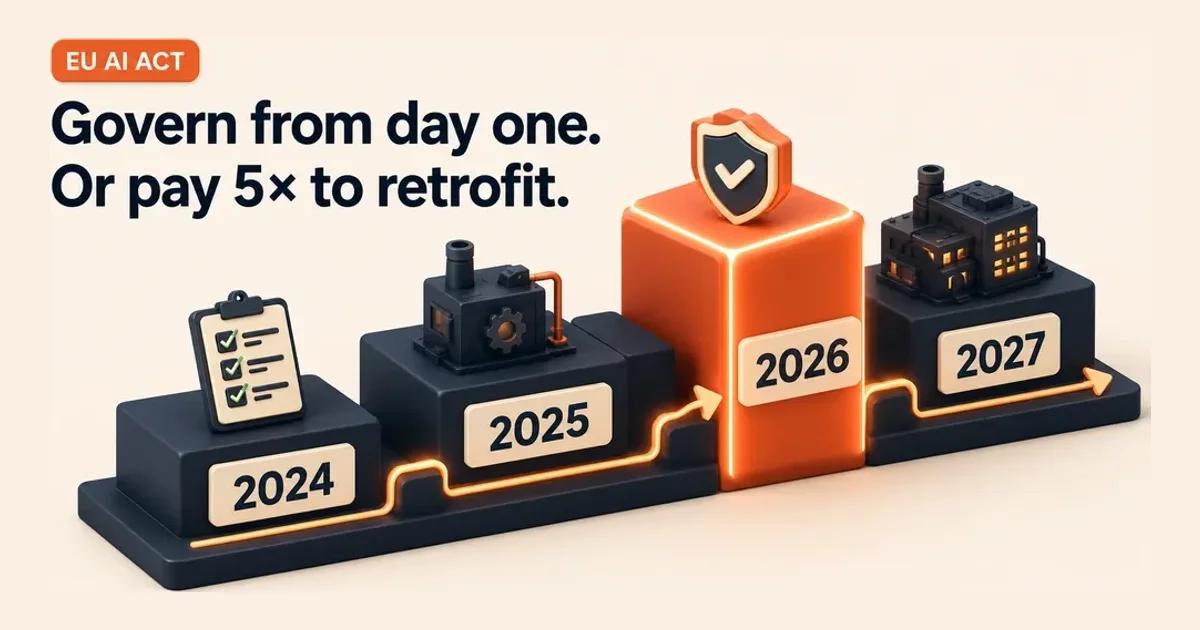
AI Governance From Day One: What Retrofitting Compliance Costs
AI regulation is converging. Firms that build AI governance in from day one avoid the GDPR-style retrofit trap that cost the last cohort several times more.